> For the complete documentation index, see [llms.txt](https://docs.ox.security/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.ox.security/ox-code/ox-code-inventory/sbom/sbom-library-details.md).
# SBOM Library Details
You can select a library from the SBOM inventory to investigate its security status, dependency relationships, package information, and known vulnerabilities.
The library details page includes the **Explore**, **General Info**, and **Vulnerabilities** tabs.
### Explore
The **Explore** tab provides an overview of the library's security and maintenance status and its relationships with other dependencies.
#### Policy status
The **Policy Status** section shows the current evaluation of the selected library.
| Check | Description |
| ----------------------- | ---------------------------------------------------------------------------------- |
| **Vulnerability Check** | Checks for known vulnerabilities associated with the library. |
| **Malware Check** | Checks whether the library is associated with known malicious packages or malware. |
| **License Check** | Checks the license associated with the library. |
| **Maintenance Check** | Checks whether the library is actively maintained. |
| **Update Check** | Checks whether a newer version of the library is available. |
| **Popularity Check** | Checks the popularity of the library. |
| **Usage Check** | Checks whether the library is used by the application. |
The panel on the right provides additional information about the library, such as its package manager, runtime status, source, license, release date, and latest available version.
#### Dependency graph
The **Dependency Graph** shows the selected library and its dependency relationships.
Use the graph to understand how the library is connected to other components in the dependency tree and whether dependencies are direct or indirect. Vulnerability indicators show where known vulnerabilities exist in the dependency path.
You can:
* Use **Show Direct Path** to display the direct dependency path.
* Use **Show All** to display additional dependency relationships.
* Select a dependency file when multiple files are available.
* Open the graph in full-screen mode.
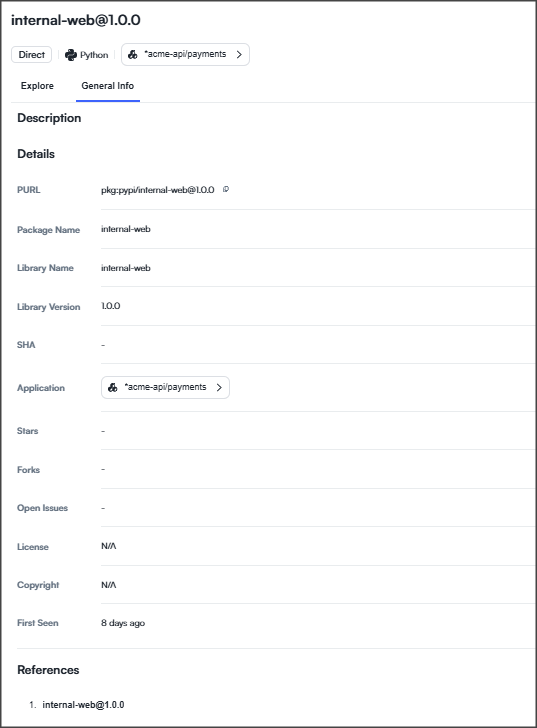
### General Info
The **General Info** tab provides metadata about the selected library, including:
* Package URL (PURL)
* Package name
* Library name
* Library version
* SHA
* Associated application
* Stars
* Forks
* Open issues
* License
* Copyright
* First seen
References associated with the library are also displayed when available.
### Vulnerabilities
The **Vulnerabilities** tab shows known vulnerabilities associated with the selected library.
For each vulnerability, you can review the vulnerability ID, affected library, runtime information, security context, discovery date, CVSS score and severity, and OX severity.
Use the search and context filters to narrow the displayed vulnerabilities.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.ox.security/ox-code/ox-code-inventory/sbom/sbom-library-details.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.